As enterprises accelerate AI adoption with Snowflake, agents are moving beyond data analysis to accessing enterprise information, executing SQL queries, invoking tools, and taking autonomous actions.
Snowflake Cortex Agents and Cortex Code enable organizations to build intelligent, data-driven workflows. But as these agents gain access to sensitive enterprise data and connected systems, security teams need visibility into what agents can access, how they behave, and what actions they take to ensure alignment with enterprise policies.
To solve this challenge, Onyx is extending our Secure AI Control Plane to Snowflake, providing agent discovery, activity monitoring, governance, and runtime enforcement across supported Snowflake agent environments as part of a unified approach to securing AI across the enterprise.
As a Snowflake Cyber Partners Community launch partner, we are excited to make this integration available to joint customers.
How Onyx Integrates with Snowflake
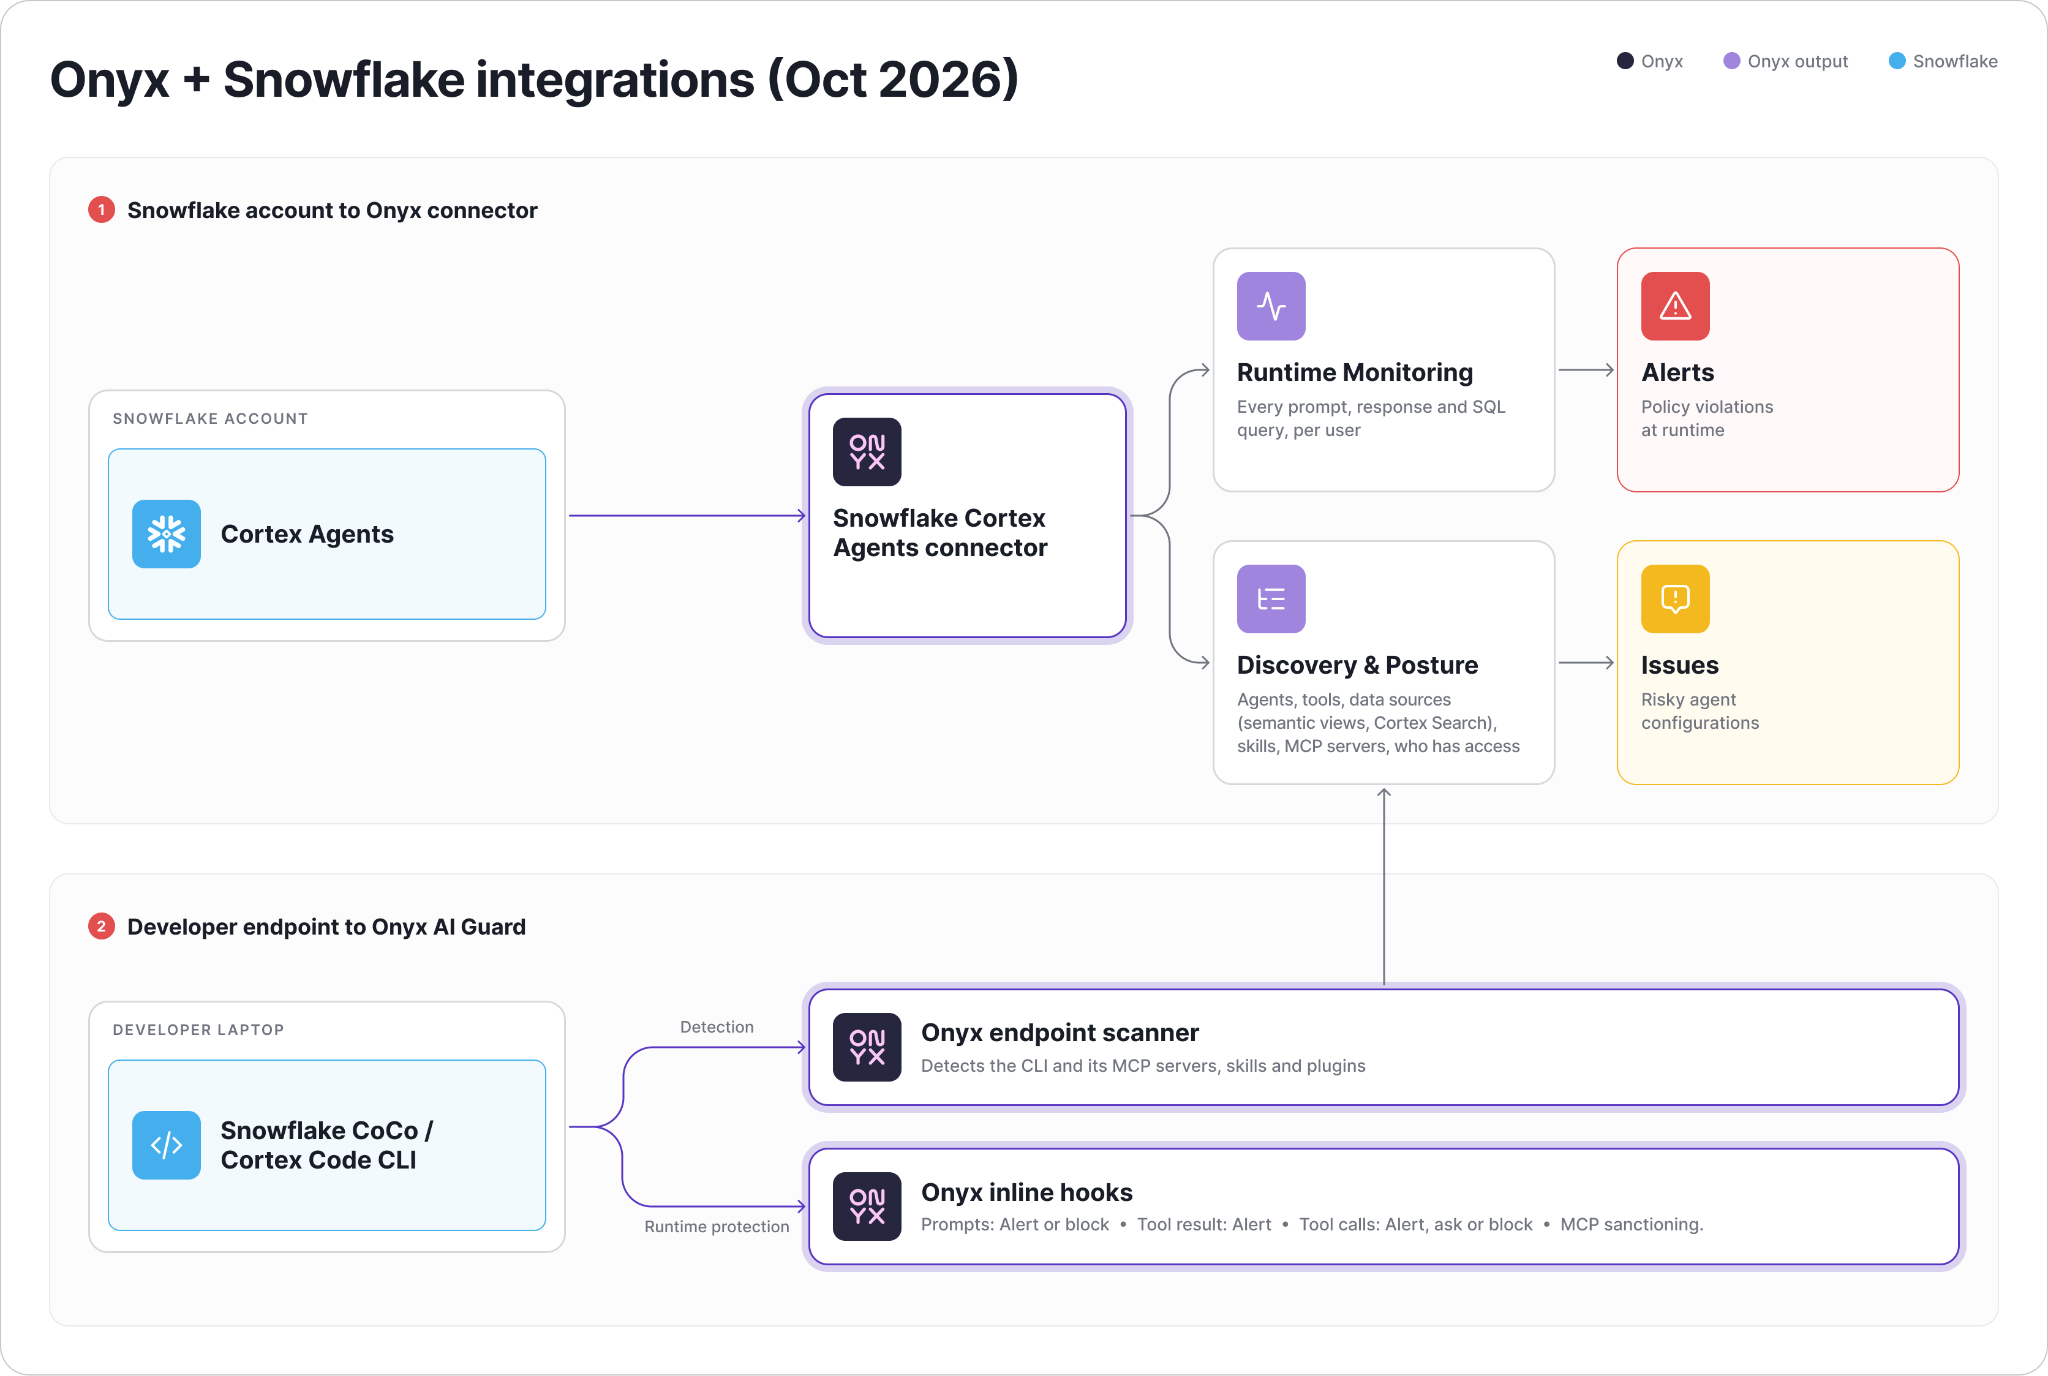
Onyx provides two complementary integrations designed to help enterprises securely adopt Snowflake’s agentic capabilities.
1. Snowflake Cortex Agents: Discover, Monitor, and Govern
Onyx integrates with Snowflake Cortex Agents to give security teams visibility into the agents operating within their Snowflake environment.
Through the integration, organizations can:
- Discover AI agents: Automatically inventory Cortex Agents across the Snowflake account.
- Map agent access and capabilities: Identify connected tools, skills, MCP servers, Cortex Search and Analyst data sources, and user access permissions.
- Monitor agent activity: Capture complete agent interaction transcripts, including prompts, responses, tool invocations, and SQL calls.
- Detect risky behavior: Evaluate collected agent activity against security policies and generate alerts for potentially unsafe or unauthorized behavior.
- Support governance and investigations: Maintain visibility into agent configurations, permissions, and historical activity to help security teams investigate risks.
This integration gives enterprises a consolidated view of their Snowflake agents within Onyx’s broader AI security environment, with periodic monitoring and policy-based alerting.
2. Snowflake Cortex Code (CoCo): Enforce Security at Runtime
For developers using Snowflake Cortex Code CLI, Onyx extends protection directly to the endpoint, where coding agents execute instructions and interact with tools.
Onyx automatically detects Cortex Code CLI activity and applies runtime security controls to:
- Inspect prompts: Evaluate developer interactions against enterprise security policies.
- Control tool execution: Block tool calls that violate security policies before execution.
- Govern MCP usage: Apply MCP server sanctioning policies to control interactions with approved and unapproved MCP servers.
- Protect sensitive workflows: Prevent policy-violating agent activity while allowing authorized development tasks to continue.
By enforcing policy at the prompt and tool-call boundaries, Onyx helps organizations move from observing agent behavior to actively controlling risky actions before execution.
One Secure AI Control Plane Across Snowflake and the Enterprise
Snowflake agents do not operate in isolation. They are part of a growing enterprise AI ecosystem spanning cloud platforms, development environments, enterprise applications, and external tools.
Onyx brings Snowflake agent visibility and governance into the same Secure AI Control Plane used to manage AI activity across the enterprise, allowing for a consistent security approach across otherwise fragmented AI environments.
Security teams gain a centralized approach to discovering agents, understanding their access, monitoring their behavior, and enforcing security policies wherever supported runtime control points are available.
The result: enterprises can accelerate agentic AI adoption in Snowflake while maintaining the visibility, governance, and control required to operate securely at scale.
Ready to secure your Snowflake agent environments? Request a demo to see Onyx in action.
Frequently Asked Questions
Onyx provides visibility and governance for Snowflake Cortex Agents and runtime protection for Cortex Code CLI. Through these complementary integrations, security teams can discover agents, understand their access, monitor activity, and enforce policies at supported runtime control points.
Onyx inventories Cortex Agents and maps their configured tools, data sources, and user access permissions. This helps security teams understand which agents are operating in their Snowflake environment and what resources they can access.
Onyx collects agent interaction records, including prompts, responses, tool invocations, and SQL calls, for periodic monitoring and investigation. It evaluates collected activity against security policies and generates alerts for potentially unsafe or unauthorized behavior.
Yes. Onyx inspects prompts against enterprise security policies and can block policy-violating tool calls before execution. It also applies MCP server sanctioning policies to govern interactions with approved and unapproved MCP servers. These runtime controls apply to supported Cortex Code CLI workflows; the Cortex Agents integration provides monitoring and policy-based alerting.
Yes. Onyx incorporates Snowflake agent visibility and governance into its Secure AI Control Plane, giving security teams a centralized view of agent activity across supported enterprise environments. Teams can investigate behavior and manage security policies, with runtime enforcement available at supported control points.